
Home / Cybersecurity Services / Security Awareness Training
CYBERSECURITY SERVICES
Security Awareness Training for Toronto Businesses
Help employees recognise suspicious messages, verify unusual requests and report concerns early. ITBizTek provides practical cybersecurity awareness training and phishing simulations for businesses across Toronto and the GTA.
Or call (416) 342-1568.
WHAT THE SERVICE COVERS
Give employees a clear response to everyday security risks
A security policy is useful only when people know how to apply it. Employees need practical examples relevant to their jobs, along with a simple reporting process when something feels wrong. Our training connects common threats with the decisions staff make around email, passwords, payment requests, shared files and remote work.
01
Recognising phishing
Practise spotting unexpected sign-in requests, suspicious attachments, document-sharing invitations and QR codes. Staff learn to consider the context of a request instead of relying only on spelling mistakes or a familiar logo.
02
Payment and supplier fraud
Help employees recognise executive impersonation and requests to change bank details. Training reinforces verification through a known contact method and the approvals required by your payment procedures.
03
Passwords and sign-in security
Explain unique passwords, password managers and multi-factor authentication in plain language. Include what to do about unexpected approval prompts and why staff should never share authentication codes.
04
Safe information handling
Discuss how employees share files, grant access and handle sensitive business information. Examples should reflect the tools your team uses and the policies the business has approved.
05
Phishing simulations
Use agreed simulated messages to understand how staff respond and where guidance is needed. Campaigns should support learning and reporting, with follow-up appropriate to the scenario.
06
Reporting and follow-up
Make it clear who employees should contact, what details to provide and why early reporting matters. Managers can review participation, simulation results and recurring areas of confusion.
BUILT AROUND YOUR BUSINESS
Build a programme around your team
New employees, experienced managers and finance staff face different requests. We discuss your roles, business applications and existing procedures before planning the training. A team handling supplier payments may need more practice with payment changes, while remote workers may need clearer guidance on account access and shared devices.
A useful programme includes an initial introduction, planned refreshers and onboarding for new starters. The schedule depends on the size of your organisation, staff availability and the risks you need to address. Short, relevant sessions are easier to apply than a long list of technical rules.
The aim is to make reporting easier. An employee who is unsure about a message should feel comfortable asking for help, and someone who made a mistake should know how to raise it promptly.
A PRACTICAL START
What a review can clarify
- Examples relevant to employee roles
- A simple route for reporting concerns
- Planned follow-up and measurable participation
HOW IT WORKS
A clear process from review to ongoing support
We agree on the scope, priorities and responsibilities before work starts.
01
Understand the audience
Review employee roles, existing policies, common suspicious messages and the tools your team uses.
02
Set a baseline
Agree on training priorities and whether an initial phishing simulation is appropriate for your organisation.
03
Train and practise
Deliver the agreed awareness topics and simulated scenarios, with a clear route for questions and reporting.
04
Review and reinforce
Use participation, reporting behaviour and simulation findings to guide refreshers and onboarding.
WHY ITBIZTEK
A local team that understands your working environment
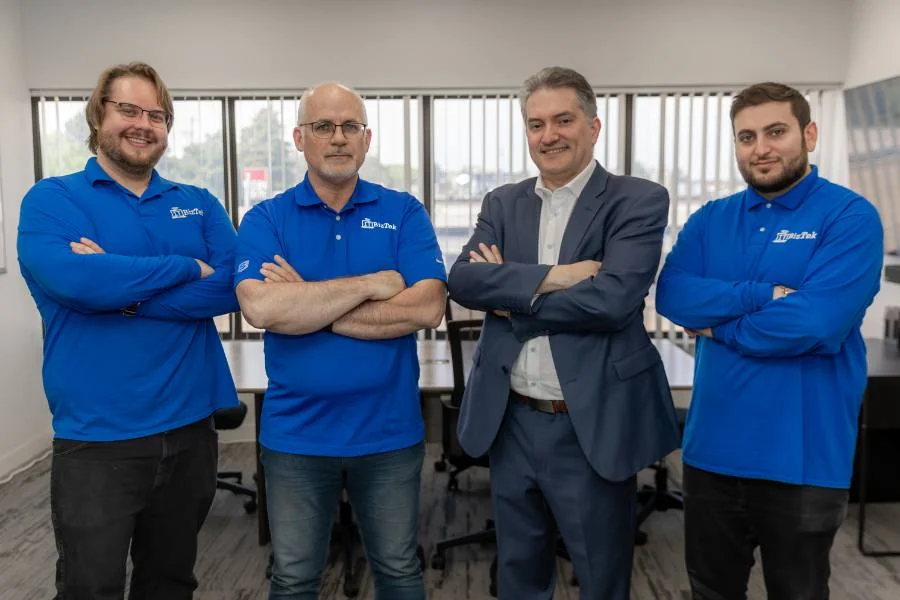
ITBizTek has supported businesses since 1998, with offices in North York and Richmond Hill. Our team connects security planning with the accounts, devices, networks and applications your employees use every day.
- Practical recommendations: review what you have before deciding what needs to change.
- Clear communication: understand the work, the next steps and the responsibilities included.
- Connected IT support: coordinate security with the wider systems your business depends on.
Learn more about ITBizTek or explore our managed IT services.
A LAYERED APPROACH
Measure learning and connect it with technical protection
Completion rates show who attended, but they do not tell the whole story. Useful measures include the number of suspicious messages reported, how quickly staff raise concerns and whether repeated scenarios show areas that need explanation. Simulation results need context: a change in message difficulty can change click rates.
Training works alongside managed email security, multi-factor authentication and endpoint protection. For software onboarding and general application instruction, visit IT staff training. Our law firm security case study shows employee guidance within a broader security project.
PLANNING YOUR SERVICE
What affects the cost?
Training costs depend on employee numbers, delivery format, topics, simulation frequency, reporting requirements and the follow-up included. We define the programme and responsibilities before work starts. If training forms part of a wider managed security agreement, the proposal identifies what is included.
YOUR QUESTIONS ANSWERED
Security Awareness Training: frequently asked questions
Have a question about your current setup? Tell us what you use today and what you want to improve.
Yes. The focus is on practical workplace decisions: recognising unexpected requests, checking messages, protecting accounts and reporting concerns. The examples and language should match the audience rather than assume IT knowledge.
It is an authorised practice campaign that sends a controlled example message to help assess and improve how employees recognise and report phishing. The scope, timing and follow-up should be agreed with the business. Simulations should never require employees to disclose real passwords.
Use an initial introduction, onboarding for new starters and periodic refreshers. The appropriate frequency depends on your risks, staff roles and results. A single completed session does not establish that an employee will recognise every future threat.
We can discuss role-specific priorities, such as payment verification, supplier impersonation, sensitive document sharing and unusual account requests. The final topics and delivery are agreed around your team.
No. Training helps people make better decisions and report concerns. Email protection, secure account access, device security and backups address other parts of the risk. A layered approach combines these controls.
Participation records and an explanation of the programme may help you answer relevant questions. Insurance requirements depend on the insurer and policy, so confirm the evidence requested with your broker rather than assuming training guarantees acceptance or coverage.
RELATED SERVICES
Build the right combination of protection
Independent guidance: Canadian Centre for Cyber Security baseline controls for small and medium organisations.
Plan Your Security Training
Tell us how many employees you have, the kinds of suspicious requests they receive and whether you already run training or phishing simulations. We will help plan a practical next step.