
Home / Cybersecurity Services / Dark Web Monitoring
CYBERSECURITY SERVICES
Dark Web Monitoring for Toronto Businesses
Find out when business credentials appear in the breach sources included in your monitoring service. ITBizTek helps Toronto and GTA businesses review exposure alerts and take practical steps to protect work accounts.
Or call (416) 342-1568.
WHAT THE SERVICE COVERS
Turn exposed-credential alerts into practical action
An employee’s work email address can appear in a breach at an unrelated website. If a password was reused, that exposure may put business accounts at risk too. Dark web monitoring looks for relevant findings in the sources covered by the service. It adds visibility into exposed credentials, while a clear review and response process helps your team decide what to do next.
01
Work email and domain coverage
Agree on the business domains and work accounts to include. Keeping this scope current matters when staff join, leave or change roles. Personal identity and credit monitoring are separate services.
02
Exposed-credential findings
Look for matches involving the agreed business identifiers in the breach and exposure sources covered by the selected monitoring service. Available findings may differ by source and do not provide a complete record of every exposure.
03
Alert review and context
Review which account appears in a finding, what information is reported and whether the source describes an older or recently discovered exposure. A new alert does not necessarily mean a breach happened recently.
04
Prioritised account protection
Assess the relevance of a finding to active work accounts. Depending on the situation, next steps may include a password reset, checking for reuse, reviewing access and strengthening multi-factor authentication.
05
Escalation when needed
Agree on who receives alerts and who is responsible for action. Signs of suspicious sign-ins or account activity may require a wider investigation, with incident support scoped around the circumstances.
06
Follow-up and scope reviews
Track the agreed actions and revisit monitoring coverage as the business changes. Review frequency, reporting and response responsibilities are confirmed in your service scope.
BUILT AROUND YOUR BUSINESS
What does a dark web monitoring alert mean?
A finding means information associated with a monitored identifier has appeared in a source covered by the service. It is a reason to assess the exposure, not proof that an attacker is currently inside your network.
For example, a work email address might appear in an old breach at a third-party website. The first questions are whether the account is still active, whether a password was exposed and whether it was reused elsewhere. An address listed without a password can still be relevant to targeted phishing.
We help put the finding into context and identify the appropriate next steps. Do not test a leaked password by attempting to sign in, or forward passwords and breach records through ordinary email. Account changes should use trusted systems and your approved IT process.
A PRACTICAL START
What a review can clarify
- Which business accounts and domains are covered
- Who reviews alerts and approves account changes
- What the monitoring can and cannot establish
HOW IT WORKS
A clear process from review to ongoing support
We agree on the scope, priorities and responsibilities before work starts.
01
Define the coverage
Confirm the business domains, accounts, authorised contacts and sources available through the service.
02
Review findings
Examine reported matches and distinguish a potential exposure from evidence of an active account compromise.
03
Prioritise the response
Agree on password, access or authentication changes and escalate suspicious activity where needed.
04
Follow up
Record agreed actions and review coverage as employees, accounts and business requirements change.
WHY ITBIZTEK
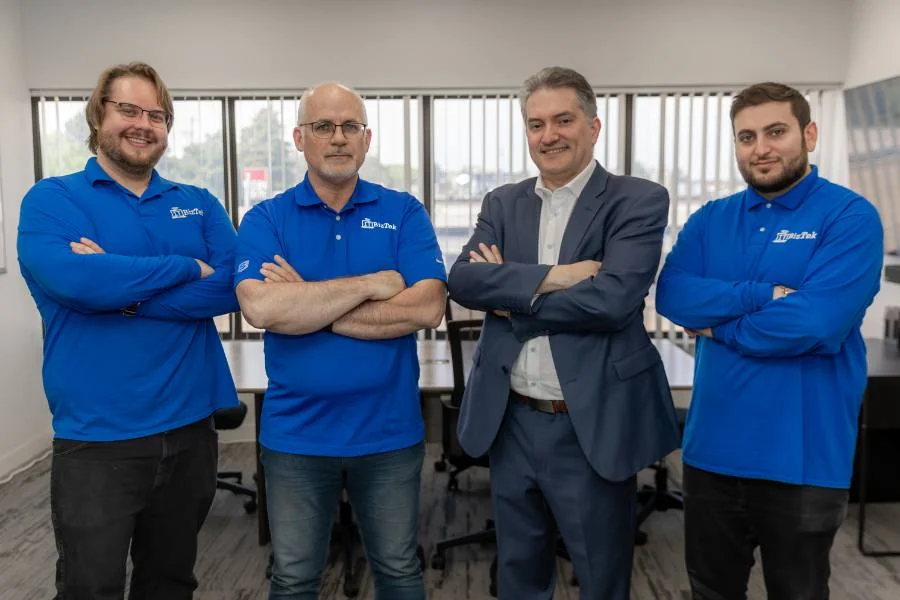
A local team that understands your working environment
ITBizTek has supported businesses since 1998, with offices in North York and Richmond Hill. Our team connects security planning with the accounts, devices, networks and applications your employees use every day.
- Practical recommendations: review what you have before deciding what needs to change.
- Clear communication: understand the work, the next steps and the responsibilities included.
- Connected IT support: coordinate security with the wider systems your business depends on.
Learn more about ITBizTek or explore our managed IT services.
A LAYERED APPROACH
Monitoring complements your existing security controls
Dark web monitoring does not block phishing messages, prevent malware or remove stolen records from every place they may have been shared. It also cannot see all private forums, encrypted groups or unpublished breach data. An absence of alerts is not proof that every account is safe.
Use it alongside email security and phishing protection, managed endpoint security and employee security awareness training. Unique passwords and multi-factor authentication help reduce the usefulness of stolen credentials.
If you need a broader review of accounts, devices and network controls, start with a cybersecurity assessment.
PLANNING YOUR SERVICE
What affects the cost?
Pricing depends on the number of business domains or accounts, the monitoring platform and source coverage, and the alert review and reporting included. We confirm the service scope before work starts. Account remediation, incident investigation and additional security projects may require separate work, so the proposal should make those responsibilities clear.
YOUR QUESTIONS ANSWERED
Dark Web Monitoring: frequently asked questions
Have a question about your current setup? Tell us what you use today and what you want to improve.
It is a service that looks for relevant information, such as exposed work credentials, in the breach and dark web sources it covers. Results depend on the provider’s visibility and agreed scope. No service can monitor every hidden source or guarantee that it will find every exposure.
Not necessarily. An employee’s work address may appear in a breach at an unrelated website. The finding needs context, including the information exposed, the source and whether the account or password is still relevant to your business.
Monitoring identifies findings; it does not guarantee removal. Copies can be retained or shared elsewhere. The practical response is to assess the risk, protect affected accounts and investigate suspicious activity where appropriate.
Employees should not send passwords to set up monitoring or respond to an alert. Coverage and any required verification are agreed through an approved process. Password resets should be completed through trusted account management systems.
Detection and notification depend on when information becomes available to the selected service and the coverage and review arrangements in your agreement. We confirm those responsibilities rather than promise instant discovery or assume every engagement includes continuous human response.
No. A vulnerability scan examines systems for potential technical weaknesses. Dark web monitoring looks for exposed information in the sources it covers. The two services address different questions and can support a wider security assessment.
It can be useful for a small business that wants additional visibility into exposed work credentials and has a clear process for acting on findings. The value depends on the accounts involved, existing controls, source coverage and follow-up included.
RELATED SERVICES
Build the right combination of protection
Independent guidance: Canadian Centre for Cyber Security guidance on credential stuffing.
Discuss Dark Web Monitoring
Tell us which business domains you use, approximately how many staff accounts you manage and who handles account security today. We will help define the appropriate monitoring scope and next steps.